Documented VPN Blocks, Reachable From the US: Five Censorship Events From a Cloud Vantage
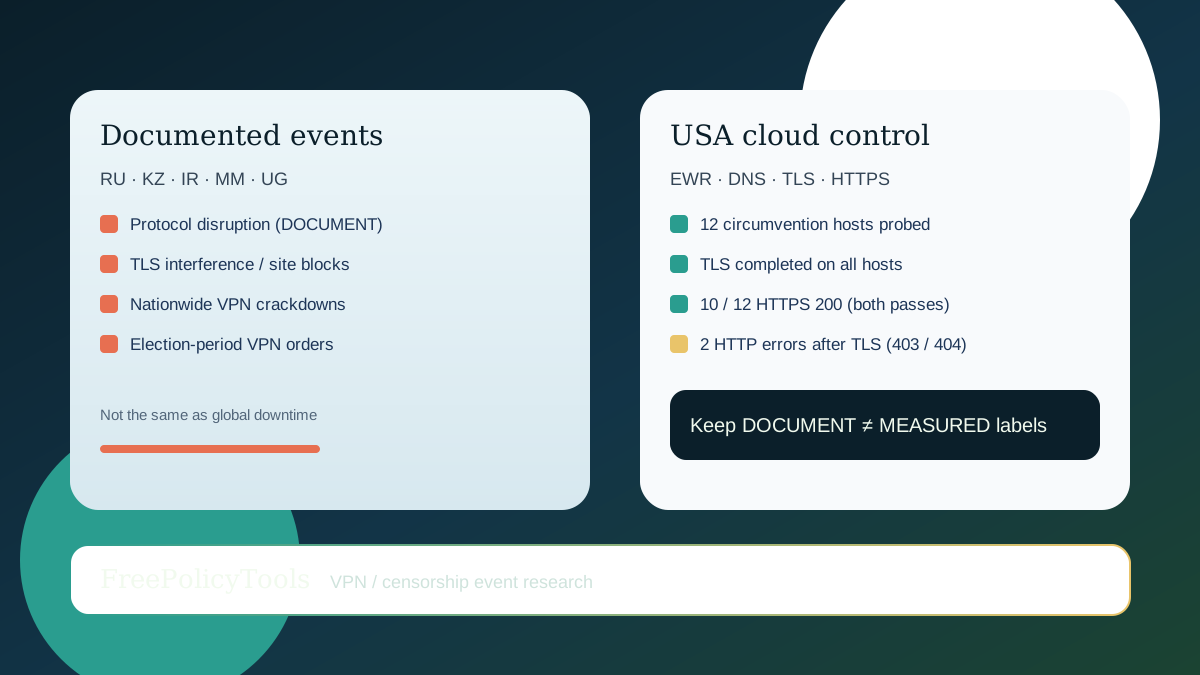
Independent reports describe VPN protocol disruption, circumvention-website blocking, and nationwide VPN crackdowns. Those documents are about specific national networks. They are not a claim that the same landing pages are dark everywhere on the Internet.
We froze five documented events, then measured DNS, TCP/443, TLSoraz HTTPS fetchability for twelve circumvention-tool websites and five source documents from a USA cloud VM (Cloudflare loc=US, colo EWR; 40 cloud-direct probes). After Runtime Secrets injected, we repeated the same frozen URL list through ProxySeller mieszkalne HTTP oraz SOCKS5h (80 residential probes; Cloudflare via proxy loc=BR, colo GRU).
From the USA cloud vantage, every frozen circumvention host completed DNS oraz TLS on both passes. Ten of twelve returned HTTPS 200. The remaining two returned destination HTTP errors after a successful handshake (NordVPN HTTP 403; Outline’s www host HTTP 404). Mieszkalne HTTP oraz SOCKS5h reproduced the same host-level pattern. All five documentation URLs were fetchable on every condition. Positive and negative controls behaved as expected.
CometVPN is treated as product and affiliate context only — we did not run a VPN tunnel and make no tunnel claims. For related FreePolicyTools work, see proxy routing research, VPN website protection warningsoraz VPN versus proxy.
Document review versus measurement
Every claim in this study carries an explicit label:
DOCUMENT— sourced from named public reports; not re-measured inside the affected country here.MEASURED_CLOUD_US— collected from this USA cloud VM with the frozen cloud-direct collector.MEASURED_PROXYSELLER_RESIDENTIAL— same frozen URLs through ProxySeller residentialHTTPorazSOCKS5hafter Runtime Secrets injected.NOT_RUN— CometVPN tunnel conditions; VPN-only product, no tunnel claim.
Mixing those layers is how readers end up believing a USA 200 OK “disproves” a Kazakhstan TLS reset. It does not. A residential HTTP 200 from a Brazil-classified egress likewise does not reproduce Myanmar DPI.
The five documented events
| ID | Zdarzenie | Warstwa |
|---|---|---|
| E1 | Russia protocol disruption (TSPU / DPI waves) | DOCUMENT |
| E2 | Kazakhstan TLS MITM + ≥73 circumvention websites | DOCUMENT |
| E3 | Iran targeted protocol crackdowns | DOCUMENT |
| E4 | Myanmar nationwide VPN restrictions (from ~30 May 2024) | DOCUMENT |
| E5 | Uganda 2021 election social + VPN website blocks | DOCUMENT |
Sources include OONI’s Russia chronicle, OONI Kazakhstan report, Filterwatch’s Iran protocol monitors, Access Now on Myanmaroraz OONI’s Uganda 2021 election post. Protocol blocks of WireGuard lub OpenVPN tunnels inside those countries remain DOCUMENT-only. Kazakhstan’s report is especially important for this study’s layer discipline: it documents both TLS interference / MITM certificates and ≥73 blocked circumvention websites, while noting Tor and Psiphon narzędzia often remained reachable — website HTTPS 200 must never be equated with tunnel success under DPI.
Full citation fields and “what we do not claim” notes are in the downloadable events-catalogue.json. Freedom House’s Myanmar FoTN 2024 entry and Human Rights Myanmar’s Great Firewall reporting complement Access Now on the May 2024 escalation.
Detailed methods and reproducibility
Platform: Cursor-hosted USA cloud agent VMs (not Kenya PC). Cap ≤7 days; this study used two same-day sessions. Cloud-direct collected (Cloudflare US/EWR, opaque egress ip_24c91b3048e7e316). Residential collected (Cloudflare via proxy BR/GRU, opaque egress ip_c722c8bf3fb76b89). /dev/net/tun was present and unused.
Frozen circumvention list (12, order fixed): nordvpn.com, www.expressvpn.com, protonvpn.com, surfshark.com, mullvad.net, psiphon.ca, www.torproject.org, www.tunnelbear.com, www.getoutline.org, www.privateinternetaccess.com, www.hotspotshield.com, www.cyberghostvpn.com.
Documentation URLs (5): OONI Russia report; OONI circumvention-reports index; Filterwatch Iran protocol monitor; Access Now Myanmar VPN ban; OONI Uganda 2021. Controls: example.com oraz wikipedia.org (expect success); nxdomain-fpt-vpn-censorship-study.invalid (expect DNS failure).
Cloud-direct collector (collect_access.py): DNS A/AAAA via dig; TCP/443; TLS handshake (version, cipher, subject CN/O, issuer O); HTTPS GET via Python urllib (follows redirects); User-Agent FreePolicyToolsResearch/1.0 (+https://freepolicytools.com/; vpn-censorship-event-study); first 64 KiB body SHA-256; truncated title; fixed timeouts in protocol.md. Two passes.
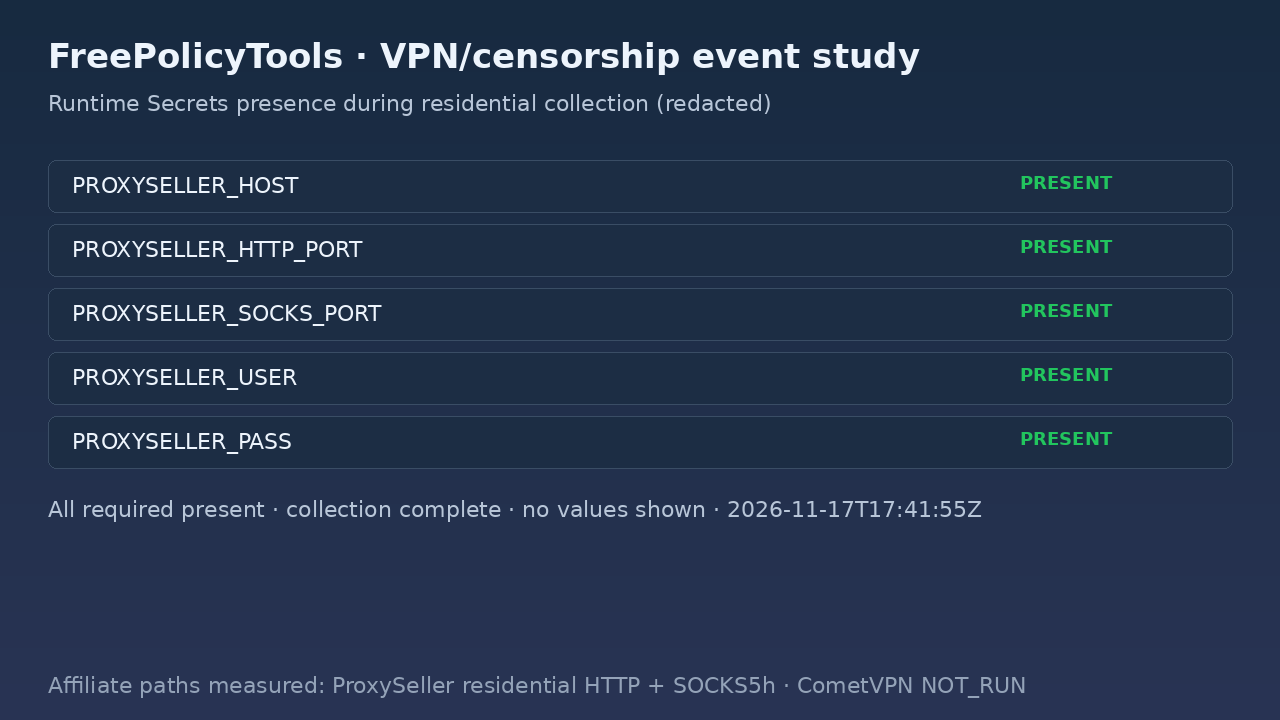
Residential collector (collect_residential.py): Runtime Secrets PROXYSELLER_HOSTPROXYSELLER_HTTP_PORTPROXYSELLER_SOCKS_PORTPROXYSELLER_USERPROXYSELLER_PASS(presence only; values never printed, committed, or placed on argv). curl with private --config proxy-user file, --location, HTTP CONNECT and SOCKS5h, same User-Agent. Local dig/TCP/TLS are not the residential path. Two passes × two transports.
Deliberately excluded: CAPTCHA solving; account creation; VPN installer downloads; third-party tunnel establishment; User-Agent rotation to bypass WAF; amending the frozen Outline www URL mid-study; inventing credentials; competitive ProxySeller uptime benchmarking; CometVPN as HTTP/SOCKS.
What we measured (charts)
Across conditions we collected 120 probes (40 cloud-direct + 80 residential). Charts below summarize outcome classes; they are not population block rates.
Where the 120 probes landed
- 20 Cloud
HTTPS 200(10×2) - 4 Cloud
TLSOK /HTTPerr (2×2) - 40 Mieszkalne
HTTPS 200(10×2×2) - 8 Mieszkalne
TLSOK /HTTPerr (2×2×2) - 30 Docs reachable (cloud+resid)
40 probes) plus residential HTTP oraz SOCKS5h (80 probes). Selected matrix — not a population block rate.Circumvention stack from USA cloud
Twelve frozen hosts; both passes agreed.
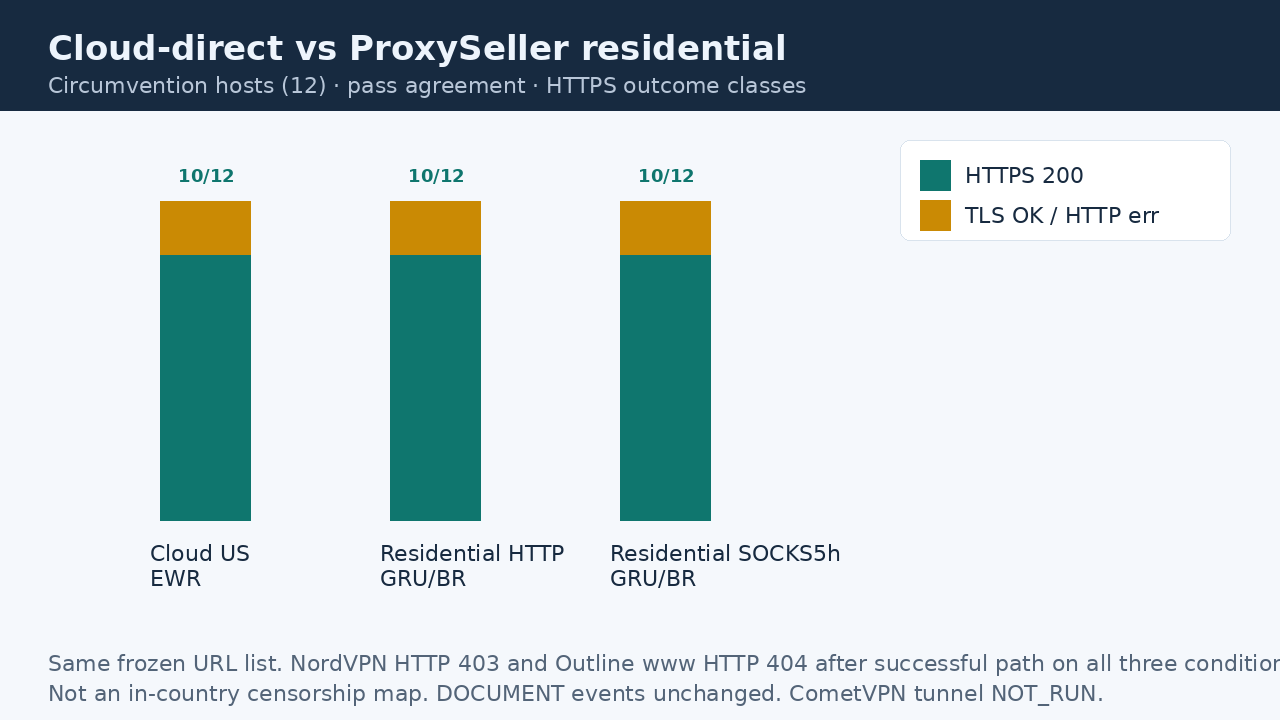
HTTPS 200 is stricter than TLS success. NordVPN HTTP 403 and Outline www HTTP 404 sit in the gap.Condition compare: HTTPS 200 vs destination HTTP errors
Same twelve hosts. Residential egress Cloudflare loc=BR, colo GRU.
Finding 1: USA cloud reachability is the wrong test for in-country VPN blocks
If a report says Kazakhstan interfered with TLS do nordvpn.com on local networks, a successful TLS handshake from a USA cloud does not refute that report. It confirms the destination still speaks TLS on the public Internet. Our two passes agreed for every primary host. Eleven of twelve hosts negotiated TLSv1.3; psiphon.ca negotiated TLSv1.2 (ECDHE-ECDSA-CHACHA20-POLY1305) on both passes. Cloud-direct reachable circumvention elapsed mean ≈ 285 ms (median 190 ms; n=20). That pattern is what an uncensored control vantage should look like — useful because it fails to mimic OONI’s anomalous block classes.
Readers comparing a USA screenshot to an OONI anomaly chart are comparing different networks. Keep the labels. Our VPN przewodnik testowy covers tunnel checks that website fetches alone cannot replace.
Finding 2: ten of twelve sites returned HTTPS 200; two failed at HTTP after TLS
| Host | Cloud | Mieszkalne | HTTP | TLS (cloud) | Issuer | Title / note |
|---|---|---|---|---|---|---|
| www.expressvpn.com | reachable | reachable | HTTP 200 | TLSv1.3 | Amazon | ExpressVPN: Best VPN Service for Speed & Privacy in 2026 |
| protonvpn.com | reachable | reachable | HTTP 200 | TLSv1.3 | Let's Encrypt | The best VPN for speed and security (residential) |
| surfshark.com | reachable | reachable | HTTP 200 | TLSv1.3 | Google Trust Services | Surfshark: identity & scam protection, antivirus, VPN |
| mullvad.net | reachable | reachable | HTTP 200 | TLSv1.3 | Let's Encrypt | Mullvad VPN - Privacy is for the people |
| psiphon.ca | reachable | reachable | HTTP 200 | TLSv1.2 | Google Trust Services | Psiphon (only frozen host on TLSv1.2) |
| www.torproject.org | reachable | reachable | HTTP 200 | TLSv1.3 | Let's Encrypt | Tor Project | Anonymity Online |
| www.tunnelbear.com | reachable | reachable | HTTP 200 | TLSv1.3 | Sectigo Limited | TunnelBear: Secure VPN Service |
| www.privateinternetaccess.com | reachable | reachable | HTTP 200 | TLSv1.3 | GoDaddy.com, Inc. | Private Internet Access: The Best VPN Service For 10+ Years |
| www.hotspotshield.com | reachable | reachable | HTTP 200 | TLSv1.3 | Amazon | Hotspot Shield: Fastest VPN for Streaming, Gaming & More |
| www.cyberghostvpn.com | reachable | reachable | HTTP 200 | TLSv1.3 | GoDaddy.com, Inc. | — |
| nordvpn.com | tls_ok_http_fail | tls_ok_http_fail | HTTP 403 | TLSv1.3 | Sectigo Limited | Just a moment… (residential) |
| www.getoutline.org | tls_ok_http_fail | tls_ok_http_fail | HTTP 404 | TLSv1.3 | Let's Encrypt | Site not found · GitHub Pages (residential) |
The NordVPN and Outline cases matter for methodology. A naive “site blocked?” script that only checks HTTP status would mark them failures and invite a censorship narrative. Transport evidence says otherwise: name resolution and the TLS handshake succeeded. See also how to unblock websites with VPNs or proxies for the separate user-facing workflow.
Finding 3: the documentation of censorship remained fetchable
All five documentation URLs returned HTTPS 200 on both cloud-direct passes and on both residential transports (30/30 documentation probes). That is not a human-rights victory metric. It shows that records about blocking oraz paths inside blocked networks are different objects. The frozen second HTML URL is the OONI circumvention-reports index; Kazakhstan’s primary DOCUMENT citation remains the English PDF in the event catalogue. Publication reachability is necessary for open science; it is not a substitute for OONI Probe vantage points.
| Documentation URL | Cloud | Resid. HTTP | Resid. SOCKS5h |
|---|---|---|---|
| Censorship Chronicles: The systematic suppression of independent media… | HTTP 200 | HTTP 200 | HTTP 200 |
| Research reports: Blocking of Circumvention Tools | OONI | HTTP 200 | HTTP 200 | HTTP 200 |
| Targeted VPN Protocol Disruption Following New Legislation | HTTP 200 | HTTP 200 | HTTP 200 |
| Worse than China or Iran? Myanmar’s dangerous VPN ban | HTTP 200 | HTTP 200 | HTTP 200 |
| Uganda: Data on internet blocks and nationwide internet outage amid 2021 election | HTTP 200 | HTTP 200 | HTTP 200 |
Finding 4: controls confirm the collector distinguishes success from DNS failure
example.com oraz wikipedia.org completed reachable outcomes on both cloud-direct passes and on both residential transports (HTTP + SOCKS5h). The synthetic .invalid name produced the expected DNS failure class on cloud-direct (TCP/TLS/HTTP skipped) and expected resolve/fetch failure through the proxy on residential legs. Without that negative control, empty DNS answers and true blocks are easier to confuse.
Finding 5: ProxySeller residential HTTP and SOCKS5h reproduced the same pattern
All five required PROXYSELLER_* Runtime Secrets were present. We ran the frozen URL list through residential HTTP oraz SOCKS5h (80 probes). Host-level outcomes matched cloud-direct: 10/12 HTTPS 200; NordVPN HTTP 403 (title “Just a moment…”); Outline www HTTP 404 (“Site not found · GitHub Pages”); docs 10/10; controls OK; pass agreement yes on both transports. Cloudflare traces via the proxy reported loc=BR, colo GRU — different from cloud-direct US/EWR — with distinct opaque egress labels (ip_24c91b3048e7e316 vs. ip_c722c8bf3fb76b89), confirming the proxy path engaged without publishing raw IPs. HTTP oraz SOCKS5h agreed on every primary host.
- HTTPS 200
- TLS OK / HTTP err
HTTP 403 and Outline www HTTP 404 after a successful path on all three conditions. Not an in-country censorship map. DOCUMENT events unchanged. CometVPN tunnel NOT_RUN.Residential website success is still not in-country evidence. If you need that egress class for researcher-operated fixtures, compare ProxySeller residential options and verify the path yourself. See also our HTTP przeciw SOCKS przewodnik.
Finding 6: CometVPN tunnel legs remain explicitly unfinished
CometVPN remains NOT_RUN — VPN-only, no HTTP/SOCKS substitute, no tunnel claim even though /dev/net/tun exists on the host. Residential proxy results are not a substitute for VPN tunnel tests against the five DOCUMENT events. Product context: CometVPN plans.
Failure classes versus OONI block signatures
| Observation here | Naive reading | Why that reading is wrong |
|---|---|---|
NordVPN HTTP 403 after TLS | “NordVPN blocked in USA / via residential” | DNS + TLS succeeded; HTTP challenge/application response (“Just a moment…” on residential) |
Outline www HTTP 404 after TLS | “Outline blocked” | TLS OK; GitHub Pages “Site not found” for frozen www host; apex separately HTTP 200 |
USA or BR residential HTTPS 200 | “Kazakhstan / Myanmar not blocking” | Wrong network; DOCUMENT events describe other ASNs and time windows |
| Docs fetchable | “Censorship overstated” | Publication reachability ≠ in-path interference |
Stosowanie OONI Explorer oraz OONI measurement documentation for in-country confirmation — not this USA/residential control package alone.
Co to badanie nie może powiedzieć
- Not an in-country map of RU/KZ/IR/MM/UG networks
- Strona internetowa
HTTPSis notWireGuard/OpenVPN/IKEv2tunnel success under DPI - Not a VPN product ranking, trust, or logging study
- Not a ProxySeller uptime or anonymity benchmark
- CometVPN tunnel
NOT_RUN - Single-day sessions; WAF and site behavior change
- Scripted
User-Agent; no CAPTCHA solve; noWebRTC/STUN
Residential reachable-probe timings (fixture only, not an SLA): HTTP mean 3459 ms (median 3076 ms); SOCKS5h mean 4279 ms (median 3472 ms).
Practical takeaways
- Read the vantage. “VPN blocked” almost always means “blocked on these networks at this time,” not “offline globally.”
- Separate website reachability from tunnel usability. Kazakhstan’s OONI write-up shows tool reachability and website blocking can diverge.
- Inspect the failure class.
HTTP 403afterTLSis not the same evidence as a handshake reset. - Use open measurement corpora for in-country claims. OONI Explorer and national partners remain the right tools for path evidence.
- Choose tools for the job. A VPN oraz residential proxy solve different routing problems; this study does not validate either against DPI.
Evidence inventory and downloads
Public: protocol, event catalogue, findings, research article, redacted cloud-direct and residential JSON, host CSVs, analysis/summary, env presence map, Outline apex-vs-www interpretive note (not in main totals), collection screenshots, ZIP + SHA-256. Private (gitignored): raw egress IPs, curl proxy-user configs, fetch body binaries, any secret material.
Reproduce with collect_access.py, collect_residential.py (requires secrets), and analyze.py.
Często zadawane pytania
Ujawnianie informacji powiązanych: This article contains ProxySeller oraz CometVPN affiliate links. FreePolicyTools may earn a commission if you purchase through them. These offers are separate from the research findings and do not change the study’s methods, results, or condition labels (MEASURED_CLOUD_US, MEASURED_PROXYSELLER_RESIDENTIAL, NOT_RUN).